3 min read

ThreatBook Recgonized in Frost & Sullivan Network Detection and Response Report as a Visionary Leader

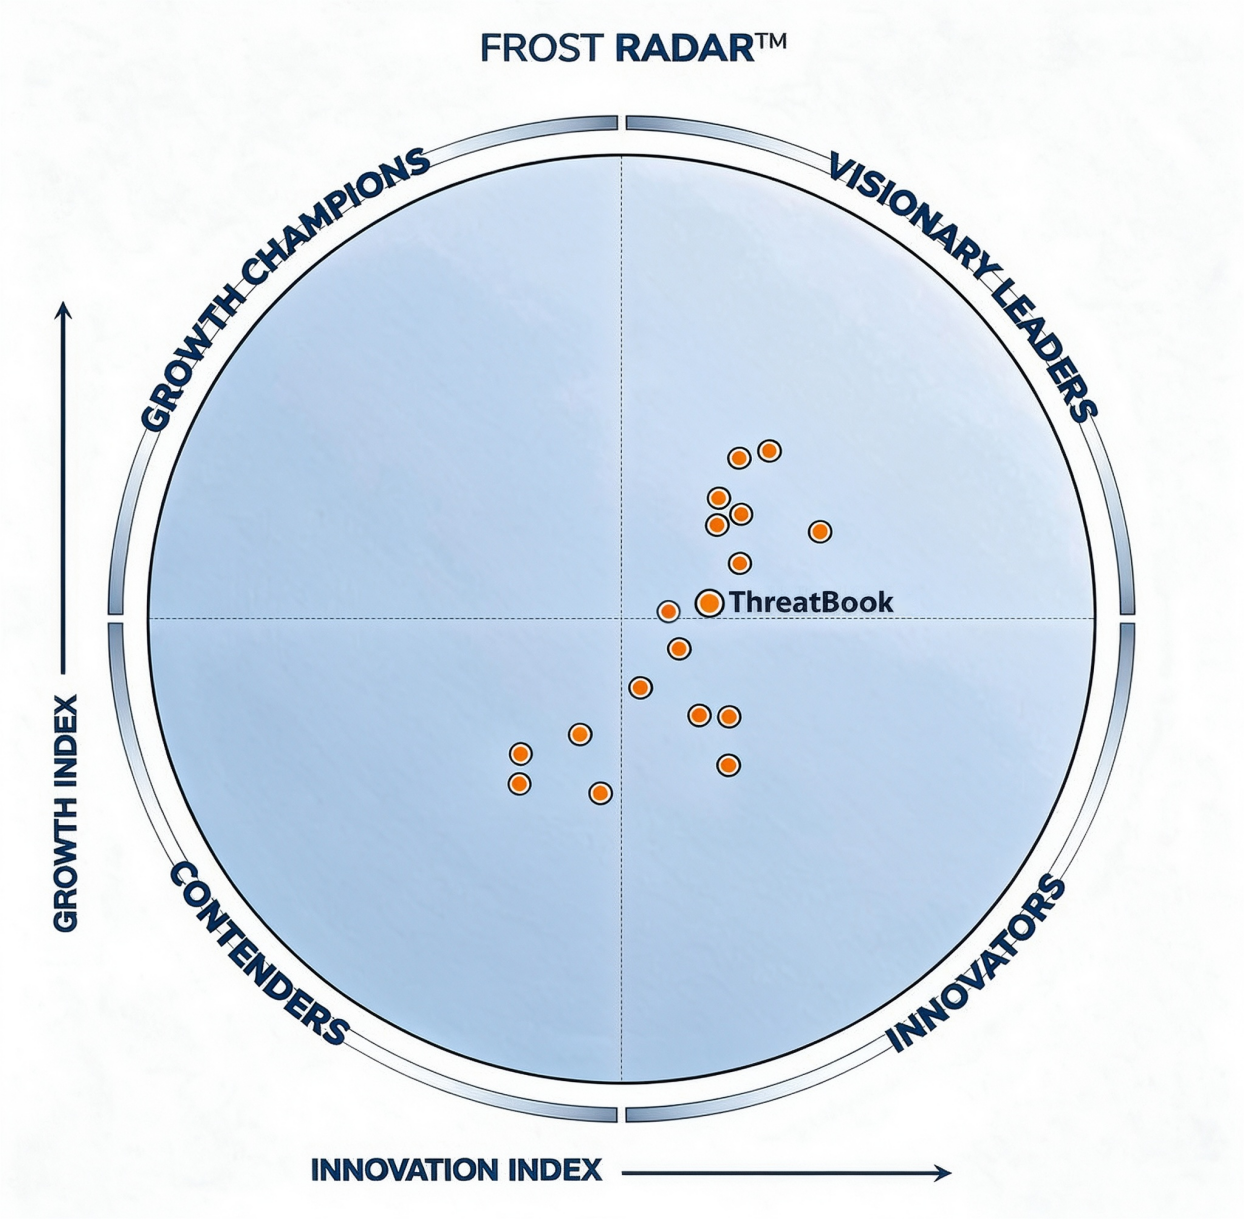
Recently, Frost & Sullivan, an internationally authoritative advisory firm, officially released the report Frost Radar™: Network Detection and Response, 2026, which systematically evaluates the growth environment, competitive landscape, and representative vendors of the global NDR market. With the leading performance of its Threat Detection Platform (TDP®), ThreatBook received a Visionary Leader rating in the Frost Radar™, and is the only domestic vendor to receive this rating.

Frost Radar for Network Detection and Response, 2026, from Frost & Sullivan. A circular chart with four quadrants: Growth Champions, Visionary Leaders, Contenders and Innovators. ThreatBook is plotted in the Visionary Leaders quadrant near the center, among other vendors shown as orange dots.

Source: Frost & Sullivan

On the Growth Index, the report finds that ThreatBook's focus on large enterprise customers aligns closely with its strong industries, such as energy and manufacturing, which has driven broad adoption of TDP in those industries, and that ThreatBook performs strongly on multiple metrics, including growth strategy. At the same time, ThreatBook is actively embracing an "agentic-first" security approach and accelerating its global business expansion in Asia-Pacific, the Middle East, and other regions, which positions it to sustain TDP's rapid growth momentum going forward.

On the Innovation Index, the report notes that NDR vendors must have differentiated advantages in distinctive scenarios, such as deep visibility, encrypted traffic analysis, native integration, investigation support, and automated response. Over the past year, TDP has introduced multiple innovative capabilities, including AI asset mapping, encrypted business service investigation, deep detection in the cloud, and dynamic cloud asset identification. It holds significant advantages in hybrid deployment and open integration, and is positioned to keep innovating and maintain its lead within an expanding security ecosystem and strategic partnerships.

Keith Beizer, Senior Analyst for Cybersecurity at Frost & Sullivan, said, “ThreatBook’s TDP unifies hybrid network visibility, threat intelligence, behavioral analytics, and automated response as the foundation for an AI-driven, agentic security ecosystem.”

Deep Visibility In and Out of the Cloud

TDP supports deployment on-premises, in multi-cloud environments, and across hybrid networks, with unified monitoring of all north-south and east-west traffic, giving users consistent network visibility and security protection. The cloud edition of TDP supports cloud traffic mirroring services and the lightweight Argus traffic diversion method, and can adapt to mainstream domestic and international cloud platforms such as AWS, GCP, Alibaba Cloud, and Tencent Cloud. It enables unified management across multiple clouds, in the cloud and outside it, and automatically tracks dynamic changes in cloud assets.

When an attack in the cloud is detected, TDP can fully reconstruct the attack chain and automatically map the attacked IP to the cloud asset it corresponded to when the attack occurred, avoiding the situation where the attacked target cannot be found after the asset has been destroyed.

Comprehensive Asset Mapping and AI Application Identification

Based on continuous traffic monitoring, TDP provides users with real-time asset discovery and attack surface identification, including AI applications.

  • AI agent risk mapping: Automatically discovers and maps AI agents and AI infrastructure deployed on office computers and local servers, along with the relay stations they connect to, and identifies the risk of exposure to the public internet and the risk of access to external agents.
  • Asset service inventory: Supports 1500+ asset service types, including ports, services, frameworks, API endpoints, application names and versions, as well as the domains and subdomains corresponding to the assets.
  • Intelligent attack surface identification: Intelligently determines enterprise vulnerability risks, and automatically identifies upload interfaces and login entry points, the external exposure of applications and services, the risk of plaintext transmission of sensitive information, the risk of AK/SK leakage, and more.

Lightweight Decryption and Encrypted Business Service Identification

TDP supports lightweight out-of-band decryption of the TLS 1.2 and TLS 1.3 protocols, including key exchange algorithms such as RSA and elliptic curve, with decryption coverage of 99% and above.

At the same time, TDP also supports mapping of private encrypted business services (non-HTTPS, with a layer of private encryption algorithm wrapped inside the body), helping users discover abnormal encrypted business services and greatly narrowing the scope of investigation for attack traffic such as encrypted webshells.

Open Integration and Flexible Automated Response

In agentic security, TDP can be connected with Flocks, the AI security operations platform, providing comprehensive network visibility for automated inspection, assessment, source tracing, and other stages.

In automated response, TDP supports powerful out-of-band blocking, with a bidirectional blocking success rate of up to 99%. At the same time, TDP also supports linkage with more than 20 mainstream third-party devices, such as SOC, SIEM, firewalls, and IPS, eliminating the response delays caused by manual operations.

In addition, TDP supports linkage with endpoint security products such as ThreatBook OneSEC. Combined with the endpoint's powerful capabilities for tracing and forensics of threat events, this pinpoints threats down to the process level and traces the source of the threat. Once the compromised endpoint has been located on the traffic side, the compromised host can be isolated directly from TDP.

With its outstanding product strength, TDP has been widely deployed among leading enterprise customers in finance, energy, manufacturing, central and state-owned enterprises, and the internet and high-tech sectors. Among internationally authoritative reports, ThreatBook was included in Gartner®'s first-ever 2025 NDR Magic Quadrant; has been included for several consecutive years (2023, 2024, 2025) in the "Strong Performer" quadrant of the Gartner Peer Insights™ Voice of the Customer for Network Detection and Response; and has repeatedly validated its real-world protection capabilities in live attack-and-defense exercises and major security assurance projects, capturing a large number of attack events such as zero-day attacks, encrypted attacks, and internal-network lateral movement.

ThreatBook stated that being named a Frost Radar™ Visionary Leader is dual recognition, from an internationally authoritative institution, of ThreatBook's product and technical strength and its quality of growth, and that it also validates ThreatBook's "technical depth plus deep scenario focus" approach. Going forward, ThreatBook will continue to focus on threat detection and, drawing on its core AI + TI capabilities, provide industry users with more trustworthy network detection and response support, leading the development of the NDR market in China and even globally.

ThreatBook Achieves 5.0 Rating in 20 Overall Responses in Gartner® Voice of the Customer for Endpoint Protection Platforms

ThreatBook Achieves 5.0 Rating in 20 Overall Responses in Gartner® Voice of the Customer for Endpoint Protection Platforms

ThreatBook achieves a perfect 5.0 rating in Gartner's latest Voice of the Customer report for Endpoint Protection Platforms, underscoring its...
Read More
Inside the Attack: Complete Technical Breakdown of the AI Ecosystem Threat Campaign

Inside the Attack: Complete Technical Breakdown of the AI Ecosystem Threat Campaign

Technical deep dive into Windows and macOS malware infection chains, detailing Indicators of Compromise for threat hunting and detection for AI...

Read More
Introducing ThreatBook ATI: From Intelligence to Fortified Defense

Introducing ThreatBook ATI: From Intelligence to Fortified Defense

ThreatBook ATI transforms raw threat data into actionable intelligence with global and APAC coverage, helping security teams detect, respond, and...

Read More